Strict data isolation
Each organisation lives in a fully partitioned space. Separation is enforced down to the database level, through three complementary mechanisms, not only in the interface. One client can never access another's data, even in the event of a mistake.
Encryption of secrets
Passwords, keys and authentication codes are encrypted. They are never stored in clear text or written to a log. Their display is time-limited and logged, and a master key protects the whole, with rotation available.
Fine-grained access control
Rights are defined by fine permissions and per organisation, never by a simple global role. Two-factor authentication, invitation-only accounts and synchronisation with your corporate directory (LDAP or Active Directory) let everyone see only what concerns them.
Protection against web attacks
The platform protects itself against request forgery, applies a strict content security policy and limits the number of attempts on sensitive actions such as login or password reset. Public routes are declared explicitly, the rest is closed by default.
Full traceability
Every important action is recorded in an audit log, without ever copying a secret value into it. You know who did what and when, which is valuable both for your clients and for your compliance obligations.
No data loss
Deletion is soft: every removed item goes to a trash and can be restored. The platform never permanently deletes business data unless you ask, which protects you from errors and mishandling.
Backups and recovery
Data is backed up in encrypted form, and continuous archiving lets you return to a precise point in time in the event of an incident. You run no risk of starting from scratch: restoring brings the platform back to the state it was in a few hours earlier.
Built-in compliance
The NIS2 and CyberFundamentals frameworks are available in the platform, with a GDPR record of processing activities. You assess your level, track gaps and gather evidence without leaving the tool you use every day.
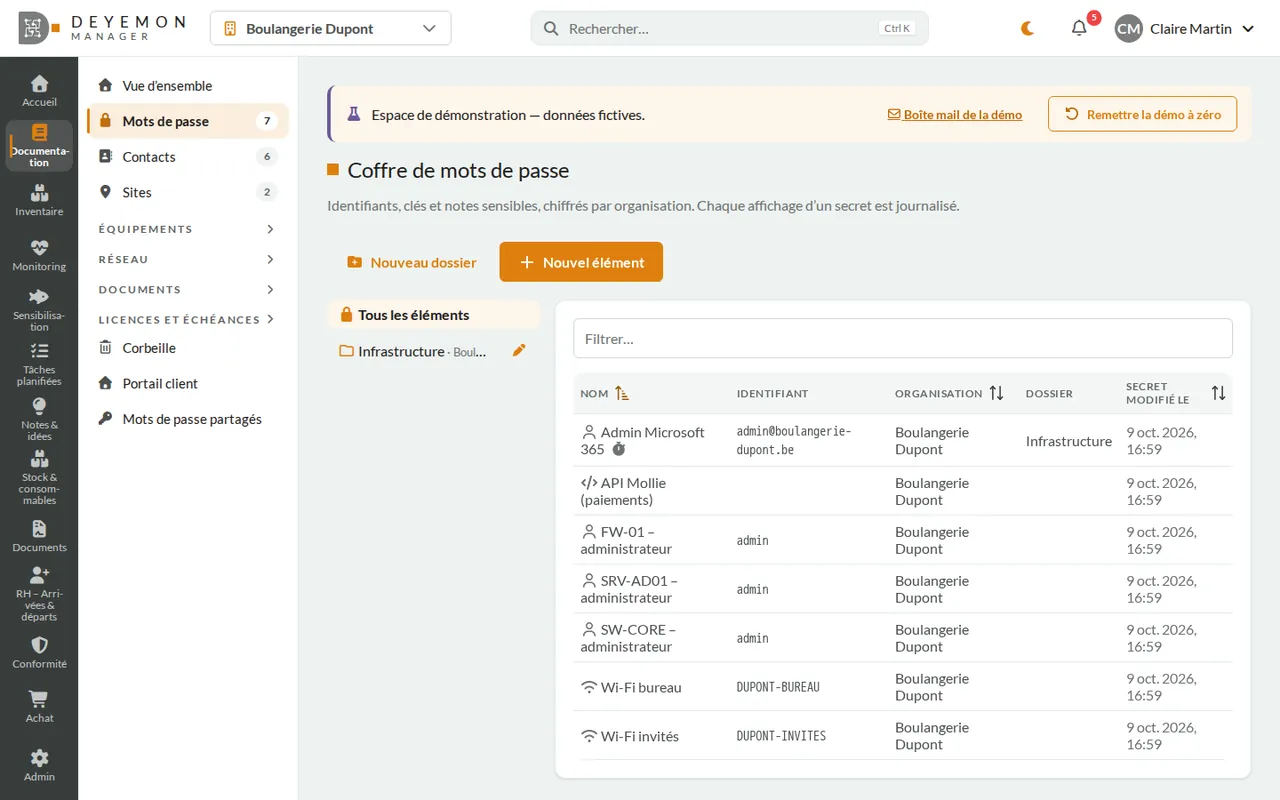
The vault, at the heart of protection
Each organisation's passwords and secrets live in an encrypted vault. You organise secrets into folders, link them to the equipment concerned, and share them by single-use link when you need to pass them to an external person.
- Encrypted secrets, never shown in clear text without a trace
- Sharing by single-use, time-limited link
- Every access is recorded